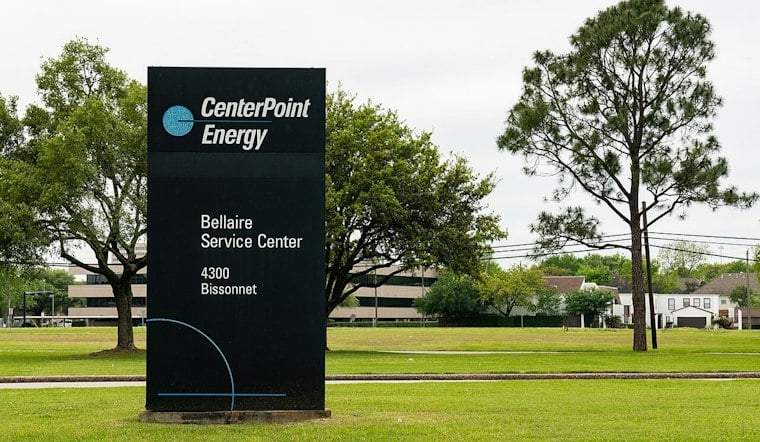
CenterPoint Energy has confirmed that a portion of its customers' personal information was stolen in a data breach earlier this month, according to a Securities and Exchange Commission filing the utility submitted on September 14. The company says an unauthorized third party obtained customer information through one of its external-facing systems, though it has not disclosed what data was taken, how the breach happened, which customers were affected, or exactly when it occurred.
As reported by ABC13 Houston, CenterPoint says it activated its cybersecurity incident response protocols after becoming aware of an online post claiming a third party had obtained a dataset containing customer information. The company says it has since launched an investigation with help from third-party cybersecurity experts, taken steps to further protect its systems, and reported the incident to law enforcement. CenterPoint maintains that its operations remain uninterrupted and that electricity or gas service was not impacted.
While CenterPoint's own filing is sparse on specifics, cybersecurity reporting has filled in far more alarming details. A threat actor using the alias 4d722e4d656f77 posted on a dark web forum on September 1 claiming to have exfiltrated roughly 7.49 million raw customer records and 6.73 million filtered records from CenterPoint, according to BleepingComputer. Those claims have not been verified by CenterPoint's official filings.
How the Data Was Allegedly Taken
Per the same report, the threat actor claimed to have pulled the dataset by cycling through customer IDs on an unauthenticated CenterPoint public application programming interface that lacked rate-limiting and web application firewall protections — a vulnerability that cybersecurity experts note is common in the utility sector. The outlet's account of the leaked dataset describes customer names, phone numbers, email addresses, service and billing addresses, account numbers, billing amounts, paperless billing status, and the last four digits of Social Security numbers, though CenterPoint has not formally confirmed which data fields were actually stolen.
CenterPoint serves approximately 7 million metered electricity and natural gas customers across Texas, Indiana, Minnesota, and Ohio, employing roughly 8,300 people and generating more than $9.3 billion in annual revenue in 2026, per the same account. The company reported net income of $244 million for the second quarter of 2026, before the breach became public, according to The Record.
Lawsuits Filed Before the Company Went Public
At least five proposed federal class-action lawsuits were filed against CenterPoint between September 10 and September 13 by law firms including Shamis & Gentile and Lippe & Associates, representing customers in Texas, Indiana, and Minnesota, according to the Houston Chronicle. The suits allege the utility failed to maintain basic data security standards — notably, that litigation began before CenterPoint's official SEC disclosure on September 14. Separately, national class-action firm Edelson Lechtzin LLP announced on September 10 that it had launched an independent investigation into data privacy claims against CenterPoint following the dark web leak, as detailed in a PR Newswire release.
CenterPoint says it is working with third-party experts to determine the scope of customers and personal information affected, and plans to notify affected customers and regulatory authorities as required by law. In its SEC filing, the company said it maintains customary cybersecurity insurance coverage that it expects will offset costs associated with the incident response and investigation.
Statutory Deadlines Keep the Clock Running
Texas law adds a firm timeline to that process. Under Texas Business and Commerce Code § 521.053, businesses operating in the state must notify affected individuals of a data breach within 60 days of determining its occurrence, and must electronically report breaches affecting 250 or more Texas residents to the state Attorney General within 30 days, according to the Fasthoff Law Firm. Separately, SEC regulations enacted in 2023 under Item 1.05 of Form 8-K require public companies to disclose a material cybersecurity incident within four business days of determining it is material — a framework relevant to evaluating the timing of CenterPoint's September 14 filing.
The breach adds to a rough stretch for the Houston-based utility, which has faced separate scrutiny this year over grid reliability and workplace safety, including a lineman death lawsuit and outages tied to summer storms. For now, CenterPoint has not disclosed when affected customers can expect formal notification, leaving millions of households across four states waiting to learn whether their information was among the records exposed.