
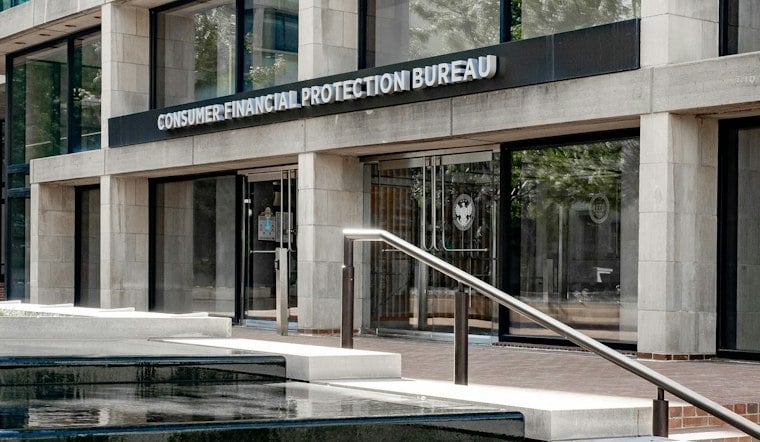
A new federal watchdog report says the security of computer equipment and sensitive consumer records left behind at four shuttered Consumer Financial Protection Bureau regional offices cannot be verified, raising fresh concerns about the safety of financial data belonging to millions of Americans. The CFPB itself has acknowledged it cannot validate the security of equipment or information stored at the abandoned locations, according to the audit.
The findings come from the Office of Inspector General for the Board of Governors of the Federal Reserve System and the CFPB, which released a report Wednesday, September 30, titled “CFPB: Hardware Assets at Former Regional Offices May Not Be Appropriately Secured.” As reported by Bloomberg, the audit warns that government databases containing sensitive financial information for millions of Americans may have been placed at risk after the Trump administration gutted the agency last year. The four abandoned regional offices were located in New York, Chicago, Atlanta, and San Francisco, and the bureau also terminated the lease on its Washington, D.C. headquarters six years early in February 2026, according to American Banker.
Then-Acting Director Russell Vought ordered the CFPB to terminate the leases on those four regional offices in 2025, Bloomberg reports, and the bureau abandoned technology assets at the sites in the process. The security of equipment or information stored at the locations could not be validated, according to the audit.
A Cybersecurity Program Already in Decline
The hardware concerns don't exist in isolation. An October 31, 2025 audit from the Federal Reserve OIG downgraded the CFPB's overall information security program maturity from Level 4, described as “managed and measurable,” down to Level 2, or “defined,” in fiscal year 2025 — and declared the bureau's cybersecurity program “not effective,” per the inspector general's own findings. The same October 2025 report found that the CFPB maintains an extensive inventory of aging, unassigned IT hardware assets lacking standardized storage, tracking, or disposal protocols, according to the Federal Reserve's oversight office.
That decline tracks with a broader thinning of the bureau's risk-management apparatus. The CFPB's Enterprise Risk Management program was placed on hold in March 2025 after the departure of former Chief Risk Officer Marianne Roth and other key risk personnel whose positions were never backfilled, American Banker reported. The pause coincided with the bureau's continued responsibility for sensitive consumer financial records.
Contracts Cut, Oversight Interrupted
In February 2025, CFPB leadership issued stop-work orders or termination notices affecting nearly all of the agency's 525 contracts, ultimately canceling 79 of them before court intervention halted further cancellations, according to an August 2026 report from the Federal Reserve inspector general. Those abrupt contract terminations severed external IT continuous-monitoring and technical support services the bureau had relied on, the same report found.
The fallout extended into the bureau's core technology systems. On June 1, 2026, the Federal Reserve OIG terminated security control reviews for three CFPB systems after discovering the agency was operating them without formal Authorizations to Operate or documented risk assessments, as required under federal FISMA regulations.
Staffing Cuts and a Forced Return to Washington
The technology troubles have unfolded alongside a sweeping reduction in the bureau's workforce. The U.S. Department of Justice submitted a court proposal in April to permanently trim CFPB staffing to roughly 556 workers, a move that would eliminate 85% of supervision staff and 80% of enforcement staff, Hoodline previously reported. The employee union NTEU has challenged the staffing cuts in federal appellate court.
Separately, internal memos issued in May ordered 1,100 employees nationwide — including 450 regional staff — to end remote telework and report in person to a new Washington headquarters at 445 12th St. N.W. by late August, according to the Consumer Finance Monitor. The building is the former headquarters of the Federal Communications Commission. CFPB Chief Legal Officer Mark Paoletta stepped in as acting director on August 1, succeeding Vought, who had led the agency's initial 2025 office closures and restructuring.
It remains unclear how, or whether, the abandoned hardware and records at the four closed regional offices will be audited and secured going forward, as ongoing litigation with NTEU and court injunctions continue to shape the bureau's operations. The bureau's own acknowledgment that it cannot validate the security of equipment at those sites leaves open the question of what, if anything, has been exposed in the meantime.