
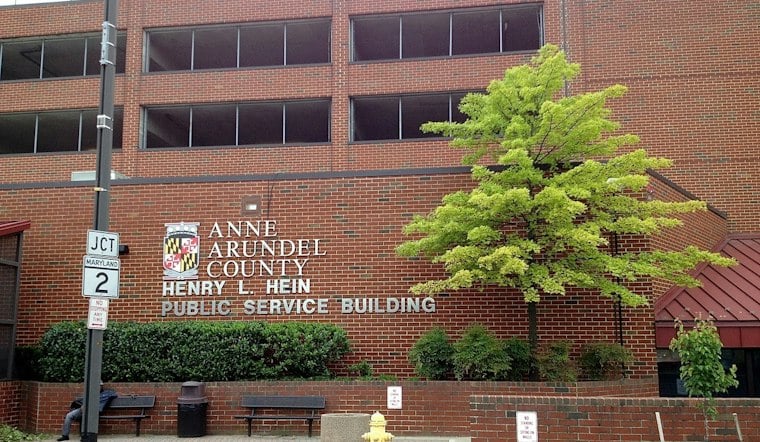
Anne Arundel County detected irregular activity on some of its computer network systems on August 28, and officials later determined that an unauthorized actor had accessed a limited number of systems and copied certain files. County Executive Steuart Pittman's office says the breach has not interfered with county operations and isn't expected to affect essential services, even as officials review exactly what was taken.
According to The Baltimore Banner, Pittman's office has not specified the type of files copied or the size of the breach, but it has said there is no indication so far that the files have been used for consumer fraud or identity theft. The county has notified federal law enforcement about the breach and is coordinating its response with investigators. Officials have also said the incident is not related to any previous cyber event affecting the county.
That caveat matters, because this is not Anne Arundel County's first brush with a major network intrusion. A separate attack in early 2025 was far more severe, forcing county government buildings to close entirely for a day in February 2025 and temporarily shutting down recycling centers and AARP tax assistance programs while IT networks were taken offline, according to the Southern Maryland Chronicle. Hoodline previously confirmed that ransomware attack compromised Department of Health records.
What Hackers Claim Was Taken
A hacker group has claimed it copied medical faxes, HR memos, and tax forms and bank data from Anne Arundel County systems, per a report on Ransomware.live. The Banner reports it could not independently verify the hacker group's claims, and county officials did not immediately answer questions about them.
The August breach unfolded while the county was still working through the fallout of the 2025 ransomware incident. Investigations into that earlier attack found that unauthorized actors accessed the county's network between January 28 and February 22, 2025, and downloaded files from the Department of Health. The county said those files may have contained names, addresses, and medical diagnoses, according to Anne Arundel County Government. The county says it will begin notifying individuals affected by that 2025 incident on October 19, more than a year and a half after the intrusion occurred.
A Pattern Across Maryland Institutions
The county's troubles have coincided with cybersecurity problems at other local institutions. Luminis Health, which operates Anne Arundel Medical Center in Annapolis, detected its own cyberattack on August 31 and didn't restore all hospital systems and its MyChart patient portal until October 8, according to Annapolis Patch. Hoodline reported on the hospital outage when it first hit, and patients affected by that breach have since filed multiple class-action lawsuits in U.S. District Court in Maryland, alleging the hospital network stored patient records in an unencrypted environment and demanding 10 years of credit monitoring, as reported by CBS Baltimore.
Cybersecurity researchers say attacks like these, where hackers steal data without locking down a victim's systems, have become more common because exfiltrated files provide ransom leverage without the disruption of a full shutdown. A 2025 threat report found extortion-only attacks, where data is stolen but no files are encrypted, had tripled to 12% of all incidents among organizations. That trend may help explain why the August breach left Anne Arundel County's day-to-day operations untouched even as files were reportedly being copied in the background.
Why the County's Systems Keep Getting Targeted
After the 2025 ransomware attack, Pittman acknowledged that the county's IT systems had been falling behind for years, a concession that led officials to budget a $4.3 million increase in IT spending for fiscal year 2026, according to Technical.ly. That investment was underway when the second breach hit in late August.
Maryland law lays out a strict chain of command for incidents like these. Local government units must report cybersecurity incidents to their local emergency manager, the State Security Operations Center within the Department of Information Technology, and the Maryland Joint Operations Center, under Maryland Code Public Safety § 14-104.1 and State Finance & Procurement § 3.5-406, per Justia Law. Separately, Maryland's Personal Information Protection Act requires entities to notify affected residents as soon as practicable, and no later than 45 days after discovering a breach, after first notifying the state Attorney General's Office.
For now, Anne Arundel County residents are left waiting on two fronts: for answers about what, if anything, was taken in the August breach, and for the October 19 notifications tied to the 2025 incident that exposed health department records. The county has said it will notify any individuals whose information is tied to the files involved in the newer breach once that review is complete.