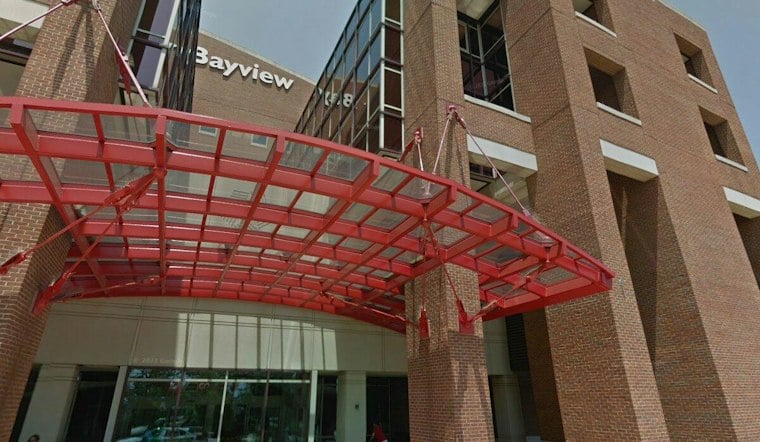
Johns Hopkins Bayview Medical Center has begun notifying about 3,182 patients that their personal health information may have been exposed after a staff member uploaded a spreadsheet of patient data to a public AI tool the hospital had not approved for that use. The exposed spreadsheet covered patients who were admitted and treated at the Baltimore hospital between May and September of this year. Letters explaining the incident started arriving in mailboxes this past Thursday.
According to WMAR 2 News, the hospital discovered the problem on September 21; during an internal review that same day, a staff member uploaded the spreadsheet to the outside AI platform. The exposed details may have included patient names, admission and treatment dates, medical record numbers, account numbers, the departments that treated patients, medications given, and the names of treating providers. The hospital says the information did not include Social Security numbers, financial account details, or other identifying information.
Once the mistake came to light, Johns Hopkins Bayview opened an investigation and says the employee deleted the AI prompt, the thread, and the uploaded document from the tool's history. The hospital also asked the AI company to delete the data from its systems, the station reports.
Credit Monitoring and a Call Center for Affected Patients
The letters mailed starting Thursday explain how recipients can sign up for 12 months of free credit monitoring through Experian IdentityWorks, and the hospital has set up a toll-free call center for patients with questions, per the same account. Patients can reach that line at 1-833-931-7766, Monday through Friday from 8 a.m. to 8 p.m. Central time, using engagement number B174716.
Johns Hopkins Bayview says it has put new measures in place to prevent similar mistakes, including strengthened policies and training around handling protected health information and limits on unapproved apps and AI tools. Staff are being retrained on which platforms the hospital has cleared for use, the station notes.
A Wider Pattern Across Hospital Systems
The Bayview incident lands amid a broader reckoning in healthcare over employees feeding sensitive records into consumer-grade AI products. A separate multi-hospital network recently deployed endpoint-based data-loss-prevention software specifically to stop patient data from reaching public AI platforms, according to itbrief.com.au. During that rollout, the system blocked hundreds of attempted transfers of sensitive information, including patient-identifiable data, medical histories, diagnoses and laboratory results, the outlet reported. That same network also built approved AI workflows so staff could still use the technology for research and administrative tasks without routing protected data through unapproved tools.
Industry survey data cited by Medical Economics helps explain why hospitals are racing to lock this down: 81% of data policy violations at healthcare organizations in 2025 involved regulated data such as protected health information, and 71% of healthcare workers were still using personal AI accounts for work tasks, down from 87% the year before. The outlet also found that 88% of healthcare organizations used cloud-based generative-AI tools, even as adoption of data-loss-prevention tools jumped from 31% to 54% over the same period.
Where HIPAA Comes In
Medical Economics reports that feeding protected health information into public AI tools can raise HIPAA concerns because many of those platforms do not sign business associate agreements or otherwise meet federal privacy standards. Under the Breach Notification Rule administered by the U.S. Department of Health and Human Services, covered entities and their business associates must notify affected individuals following a breach of unsecured protected health information, which the agency defines broadly as an impermissible use or disclosure that compromises the security or privacy of that data.
The Bayview case is not an isolated flashpoint for the industry. Engineers at Epic reportedly deployed an Anthropic tool that exposed security risks potentially allowing undetected access to millions of patient records, according to low-confidence reporting from the New York Times, underscoring how even established health records vendors are grappling with the same AI-era vulnerabilities now playing out at a single Baltimore hospital.