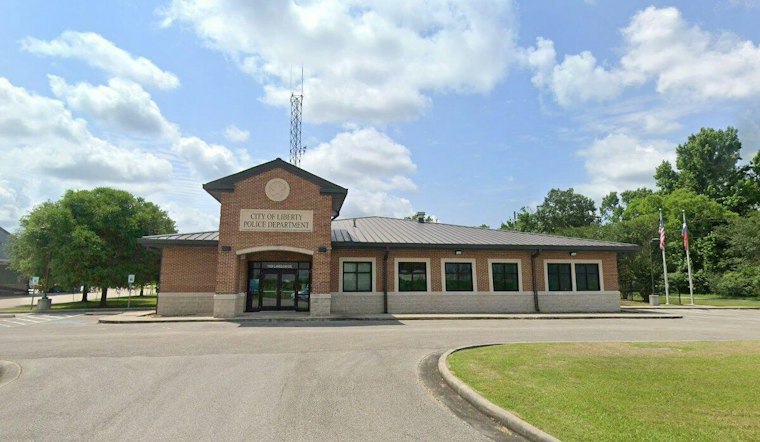
The City of Liberty, Texas was defrauded of approximately $600,000 after staff wired funds to a fraudulent account following an email that appeared to come from a legitimate vendor. The payment request landed in city inboxes from an address designed to mimic that vendor's real domain, and because Liberty genuinely owed that vendor a debt in the same dollar amount, staff initially evaluated the request as valid before approving the transfer.
City officials explained the mechanics of the scam in an official statement reported by Click2Houston, noting that the matching invoice amount was central to why the request passed initial scrutiny. According to that same account, the scheme appears to have originated from an outside source that created a fake email domain closely resembling the vendor's actual address, rather than from any breach of Liberty's own computer network, which the city says remained uncompromised.
Bank Flagged the Transfer Too Late
The receiving bank alerted the city's bank that the transfer looked potentially fraudulent, but by the time that warning went out, the wire had already gone through, the station's report notes. Liberty's police department is now working with federal law enforcement agencies on the investigation, and federal investigators are involved in examining the Liberty case directly. City officials say they do not suspect wrongdoing by the city itself, the vendor, or any of the city's consultants.
Liberty has filed a claim with its insurance carrier over the incident and says it has strengthened its vendor payment verification procedures going forward, per the same Click2Houston account. Officials say they will continue cooperating fully with federal law enforcement but cannot share additional details while the investigation remains open.
Why These Scams Keep Working
City of Liberty's experience fits a pattern authorities have been warning about for years: Business Email Compromise attacks succeed not by hacking networks but by exploiting routine invoice workflows and legitimate business context. According to FBI Internet Crime Complaint Center data reported by STACK Cybersecurity, this type of fraud caused $3.05 billion in reported losses across more than 24,000 complaints nationwide in 2025, making it the second-costliest cybercrime category behind investment fraud. A report from NINJIO found that cyber-enabled fraud categories accounted for roughly 85 percent, or $17.7 billion, of all financial losses reported to the FBI last year.
The threat extends well beyond any single city. A 2026 treasury practitioner survey cited by DeepStrike found that 74 percent of organizations that experienced payment fraud reported being targeted by attempted or actual Business Email Compromise, with these attacks frequently aimed at invoice approvals and wire transfer workflows specifically. In August 2026, the City of Fort Worth issued its own public alert about fraudulent email payment requests mimicking city departments, explicitly warning residents and contractors that the city never requests payment by wire transfer, as reported by the Fort Worth Business Press.
Texas Rules and a Tough Recovery Road
Texas law already requires local government employees who access municipal computer systems to complete annual cybersecurity awareness training certified by the Texas Department of Information Resources, under Texas Government Code Section 2054.5191, according to safemode IT. Lawmakers have since gone further: the state expanded its training mandates under Section 2054.5193 to require annual certified artificial intelligence awareness training for local government personnel as well, as reported by the Evolve AI Institute.
Recovering money once a fraudulent wire like this clears can be extraordinarily difficult. Small business financial platform Nav notes that funds-transfer and social engineering fraud are among the most frequent cyber insurance claims filed by small organizations, but misdirected funds become very hard to recover once a transfer is finalized. Texas courts have also weighed in on who bears the loss when these scams succeed: a 2022 Texas Supreme Court decision in Cadence Bank, N.A. v. Elizondo, analyzed by law firm Porter Hedges LLP, found that standard administrative wire transfer forms generally do not alter the default liability allocation under deposit agreements and the Texas Uniform Commercial Code when email wire fraud occurs.
Liberty is far from the first Texas municipality targeted this way. In a case Hoodline covered in October 2024, federal prosecutors indicted seven people, including residents of Houston and Austin, for running a nationwide Business Email Compromise conspiracy that used spoofed emails to redirect wire transfers from municipal and private sector victims alike. For now, Liberty officials say the investigation remains active, and they are not releasing further details until federal authorities complete their work.