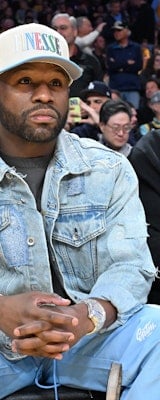

A Hollywood, Florida man who built a business telling cyberattack victims he could unlock their encrypted files without paying ransom is now accused of doing exactly that behind their backs — and charging them millions more than what he handed over to the hackers. Zohar Pinhasi, 50, surrendered to federal authorities in Brooklyn on Wednesday and pleaded not guilty to wire fraud conspiracy and wire fraud charges tied to his company, MonsterCloud LLC.
Pinhasi, who also went by the names Zack Silver and Zack Green, was released on a $2 million bond following his arraignment before U.S. Magistrate Judge Peggy Cross-Goldenberg, according to the Department of Justice. A federal grand jury in the Eastern District of New York returned the indictment on September 23, charging him with one count of wire fraud conspiracy and two counts of wire fraud spanning June 2018 through June 2023 — each count carrying a maximum sentence of 20 years in prison.
MonsterCloud marketed itself as an alternative to paying ransom after a cyberattack, telling clients it could recover encrypted data through advanced decryption techniques and proprietary tools, according to CBS12. Prosecutors allege Pinhasi had no special technology to decrypt the data at all. Instead, he is accused of contacting the hackers responsible for the attacks, paying their ransom demands himself, and then charging clients substantially more than what he paid.
The Markup: From $8,200 to $150,000 in One Deal
In one transaction detailed in the case, Pinhasi allegedly paid about $8,200 to a cybercriminal in August 2023 to obtain a decryption key, then billed the client roughly $150,000, per the station's report. A separate transaction described in court filings shows an even wider spread: MonsterCloud paid roughly $236,000 to cybercriminals for a decryption key in one case, then billed the victimized business approximately $380,000 for data restoration, according to BleepingComputer.
Taken together, federal prosecutors say MonsterCloud charged clients more than $19 million and facilitated over $8 million in ransom payments to cybercriminals, the Department of Justice said. The company billed hundreds of victimized companies across the United States and Canada over the course of the alleged scheme, illustrating just how widely the business reached across North American commercial clients.
Fake Proof and a Contract Designed to Cover Tracks
Federal prosecutors further allege that MonsterCloud obtained sample decrypted files directly from the extortionists and passed them off to clients as proof of its own technical recovery work, according to Circuit Magazine. Those sample files were reportedly used as recovery proofs to convince victims that MonsterCloud's own tools, not a hacker's cooperation, had done the work.
Court filings also show that while some MonsterCloud contracts disclosed the company might communicate with or pay attackers, those contracts framed the practice as a last resort used only after technical tools failed. Prosecutors allege contacting attackers was usually the firm's first step, not its final option, the outlet's report notes. MonsterCloud also used testimonials that included paid spokespeople, CBS12 reported, bolstering the company's public image as a legitimate technical alternative to ransom payment.
U.S. Attorney Joseph Nocella Jr. said Pinhasi falsely claimed to decrypt ransomware without paying ransomers and re-victimized clients while extracting a hefty profit. Pinhasi has pleaded not guilty to all charges and is presumed innocent unless proven otherwise.
Warning Signs Dated Back Seven Years
This is not the first time MonsterCloud's practices drew scrutiny. A May 2019 investigation by ProPublica reported that Coveware CEO Bill Siegel used the phrase “ransomware payment mills” for a group of firms that included MonsterCloud, and that cybersecurity researchers suspected the company was quietly paying attackers while claiming to use trade-secret decryption technology. ProPublica reported that Pinhasi described MonsterCloud's recovery methods as varying by case and as a trade secret. CBS12 separately reported an alleged 2019 message in which Pinhasi said the company did not have proprietary ransomware-decryption technology.
Before his arrest, Pinhasi, a U.S. and Israeli national, frequently gave media interviews presenting himself as a cybersecurity expert, publicly advising crime victims against paying ransoms, according to The Jerusalem Post. That public posture stands in sharp contrast to the conduct prosecutors now allege.
Why the Case Matters Beyond One Company
The prosecution is being handled by the Justice Department's Computer Crime and Intellectual Property Section alongside Eastern District of New York prosecutors, arriving as the FBI and the Cybersecurity and Infrastructure Security Agency continue urging ransomware victims not to pay attackers. Paying ransoms can also create sanctions liabilities under federal regulatory frameworks, a consideration that looms over any company that facilitates such payments on a client's behalf.
The case underscores the importance for business owners hit by ransomware of independently verifying third-party remediation firms' claims about decryption. It remains unclear whether client insurance providers covered the inflated invoices described in the indictment, or whether civil subrogation lawsuits or regulatory action from agencies such as the Office of Foreign Assets Control could follow — questions that remain open as the criminal case moves forward.